








php 8.6读取pkcs12证书包时,openssl_pkcs12_read接收的是文件内容和解锁口令,成功后从结果中分别取得证书与私钥。私钥不应直接打印或保存到站点目录;下面把它重新用独立口令加密导出到权限受限的新文件。
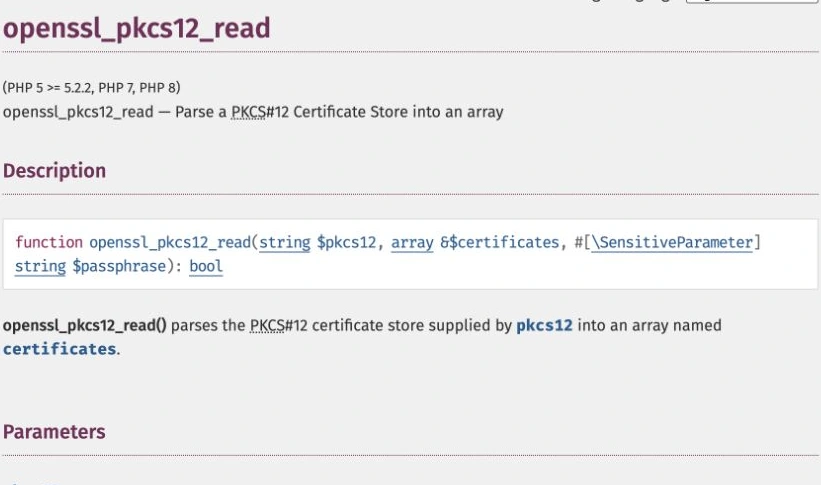 。图源:PHP Documentation Group(CC BY 3.0)。
PHP手册中的openssl_pkcs12_read。图源:PHP Documentation Group(CC BY 3.0)。
解析证书包并加密导出私钥
<?php
$dir=realpath('/srv/app-private/cert-output');
$oldPass=getenv('P12_PASSWORD');$newPass=getenv('PEM_PASSWORD');
if(!$dir||!is_writable($dir)||!is_string($oldPass)||!is_string($newPass)||$newPass==='')throw new RuntimeException('配置不完整');
$raw=file_get_contents('/srv/app-private/client.p12',false,null,0,4194305);
if(!is_string($raw)||strlen($raw)>4194304)throw new RuntimeException('证书包无效');
if(!openssl_pkcs12_read($raw,$certs,$oldPass))throw new RuntimeException('证书包解析失败');
if(!isset($certs['pkey'],$certs['cert']))throw new RuntimeException('证书包缺少私钥或证书');
$key=openssl_pkey_get_private($certs['pkey']);
if($key===false)throw new RuntimeException('私钥解析失败');
$private=tempnam($dir,'key-');$certificate=tempnam($dir,'cert-');
if($private===false||$certificate===false)throw new RuntimeException('输出文件创建失败');
$ok=false;
try{
if(dirname($private)!==$dir||dirname($certificate)!==$dir)throw new RuntimeException('输出目录偏离');
if(!openssl_pkey_export_to_file($key,$private,$newPass))throw new RuntimeException('私钥导出失败');
if(file_put_contents($certificate,$certs['cert'])!==strlen($certs['cert']))throw new RuntimeException('证书写入失败');
if(!chmod($private,0600)||!chmod($certificate,0600))throw new RuntimeException('权限设置失败');
$ok=true;echo "证书与加密私钥已分别保存到私有输出目录\n";
}finally{if(!$ok){if(is_file($private))unlink($private);if(is_file($certificate))unlink($certificate);}}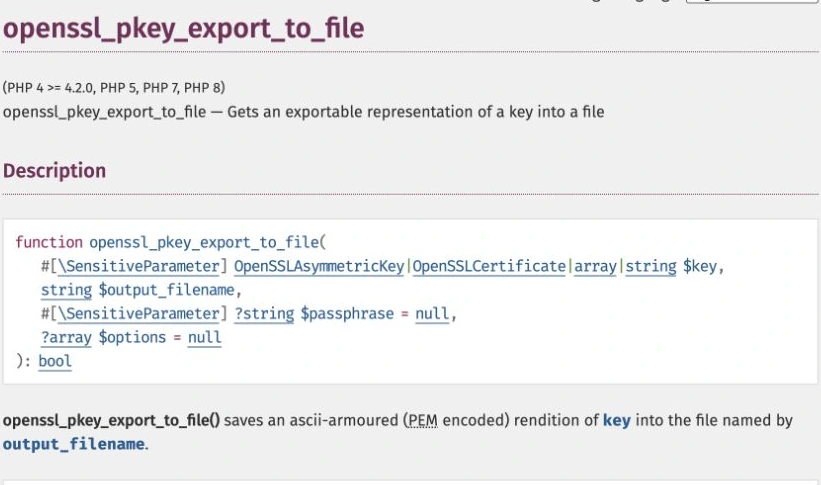 。图源:PHP Documentation Group(CC BY 3.0)。
PHP手册中的openssl_pkey_export_to_file。图源:PHP Documentation Group(CC BY 3.0)。
私钥口令与证书信任分别处理
输出目录应提前由管理员创建并限定应用账号访问,Unix下建议0700;Windows还需按实际ACL限制。成功解析不能证明证书链可信、证书未过期或用途匹配。包内extracerts如需保存,要作为中间证书集合明确处理,不把它们自动设成受信根。

Build MCP servers and clients for PHP applications with the official PHP SDK
下载
使用官方Model Context Protocol PHP SDK将PHP应用程序功能暴露为MCP工具、资源和提示,用于代理工作流。
处理旧算法和失败输出
某些旧PKCS12包使用当前OpenSSL配置未启用的算法,失败原因应在服务端安全记录中检查,优先让签发方重新导出兼容证书包;不要在公开响应中输出私钥、口令或完整证书包。重新加密只改变私钥的保存方式,不会续签证书或改变有效期。




















